From Keyword to Code
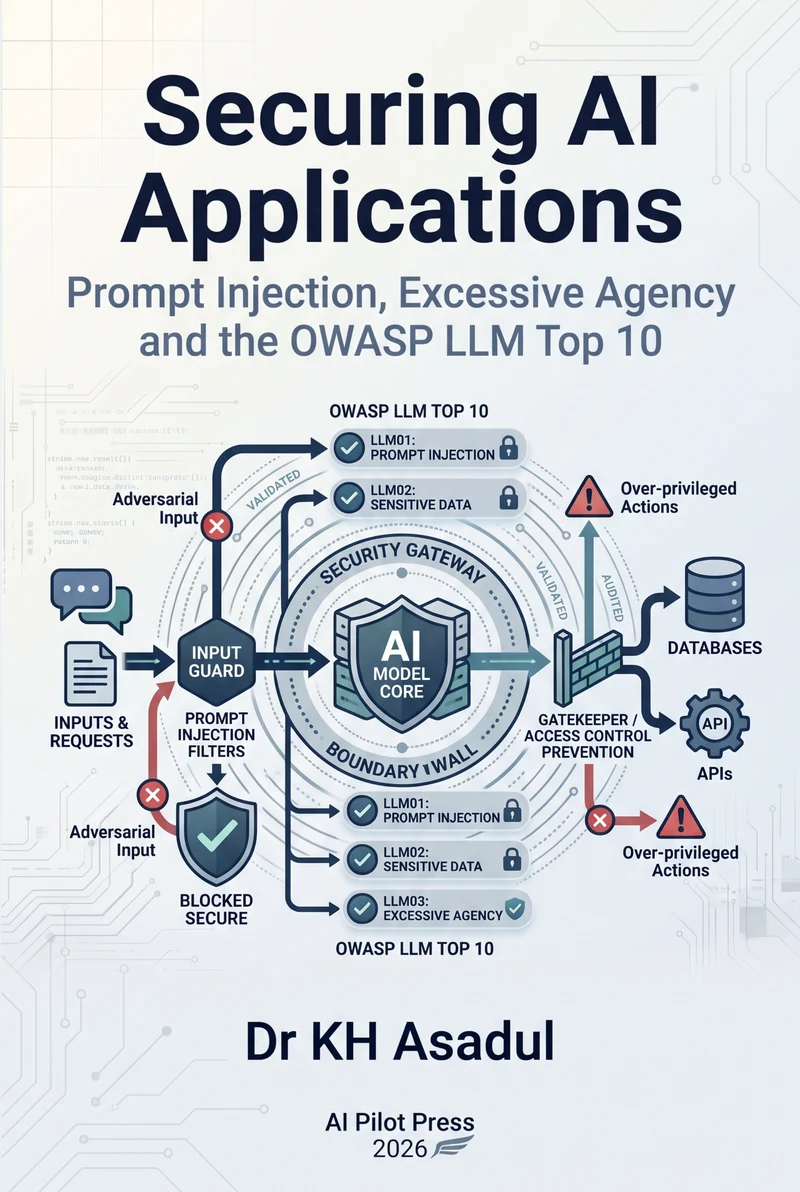
Securing AI Applications
Prompt Injection, Excessive Agency and the OWASP LLM Top 10
Recognise common security risks in language-model applications and design controls around data access and tool permissions.
Who it’s for
Developers building applications on top of language-model APIs.
Opens Amazon in a new tab. Check the listing for formats and availability.
A closer look
About this book.
Work through the OWASP LLM Top 10 from a developer’s perspective. The book translates risk categories into a threat model for a feature, with attention to what the application can read and what actions it can take.
Reader resources.
Official documentation and guides for topics covered in this book.
← Back to the books